Aegis
A privately distributed, open-source threat and cyber intelligence platform. One operational picture, assembled from the open internet.
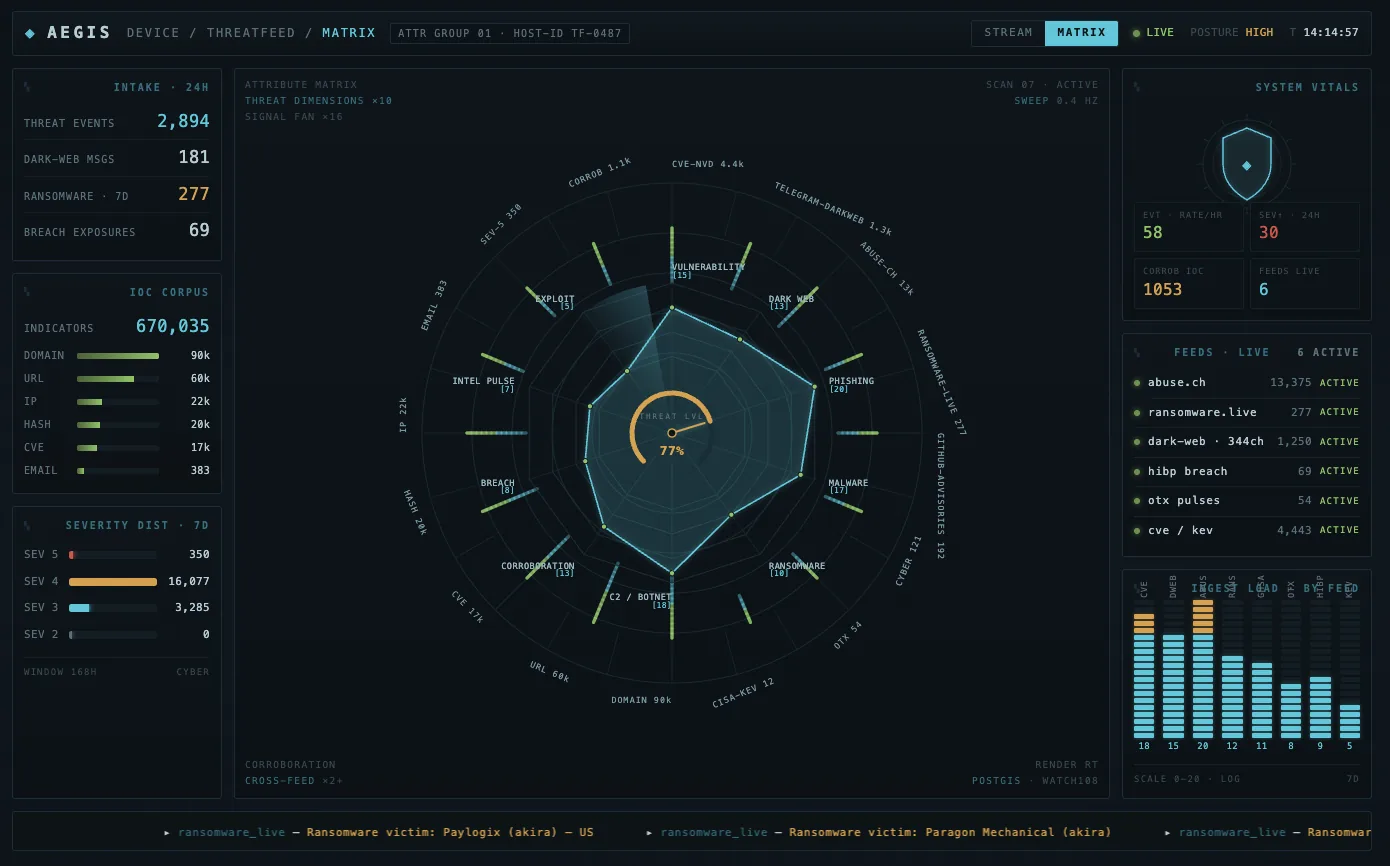
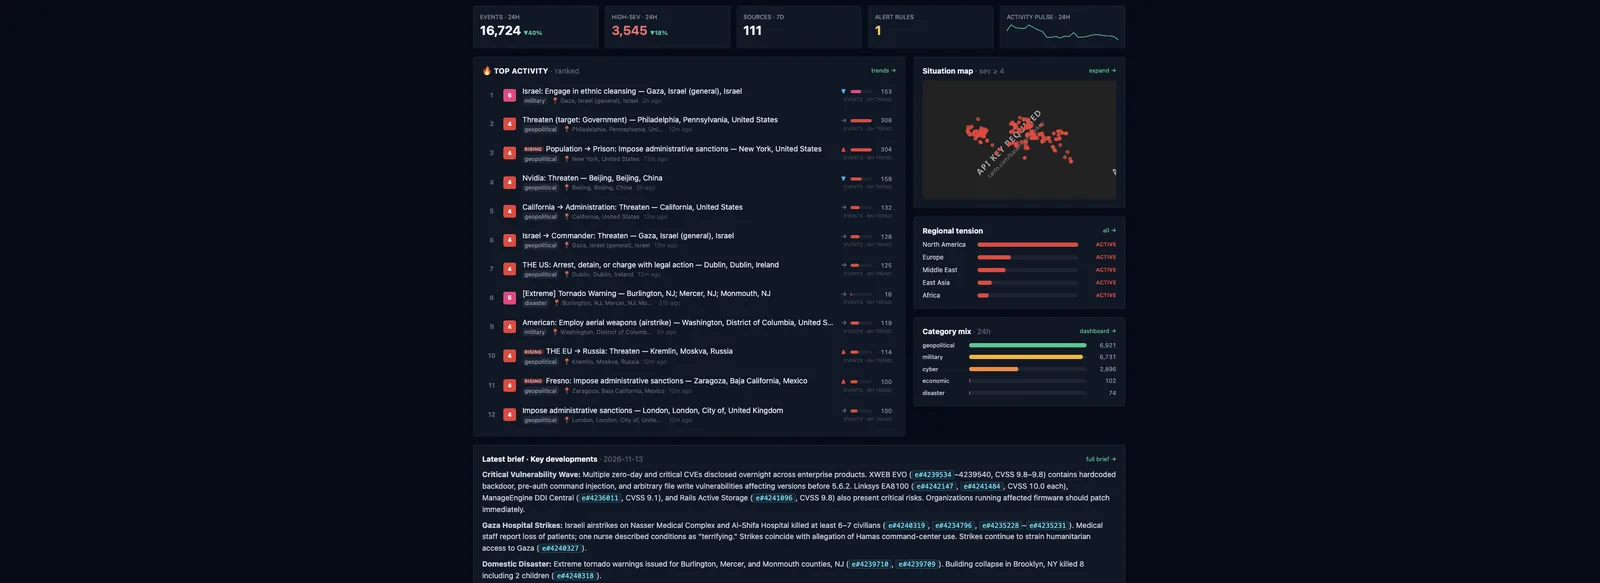
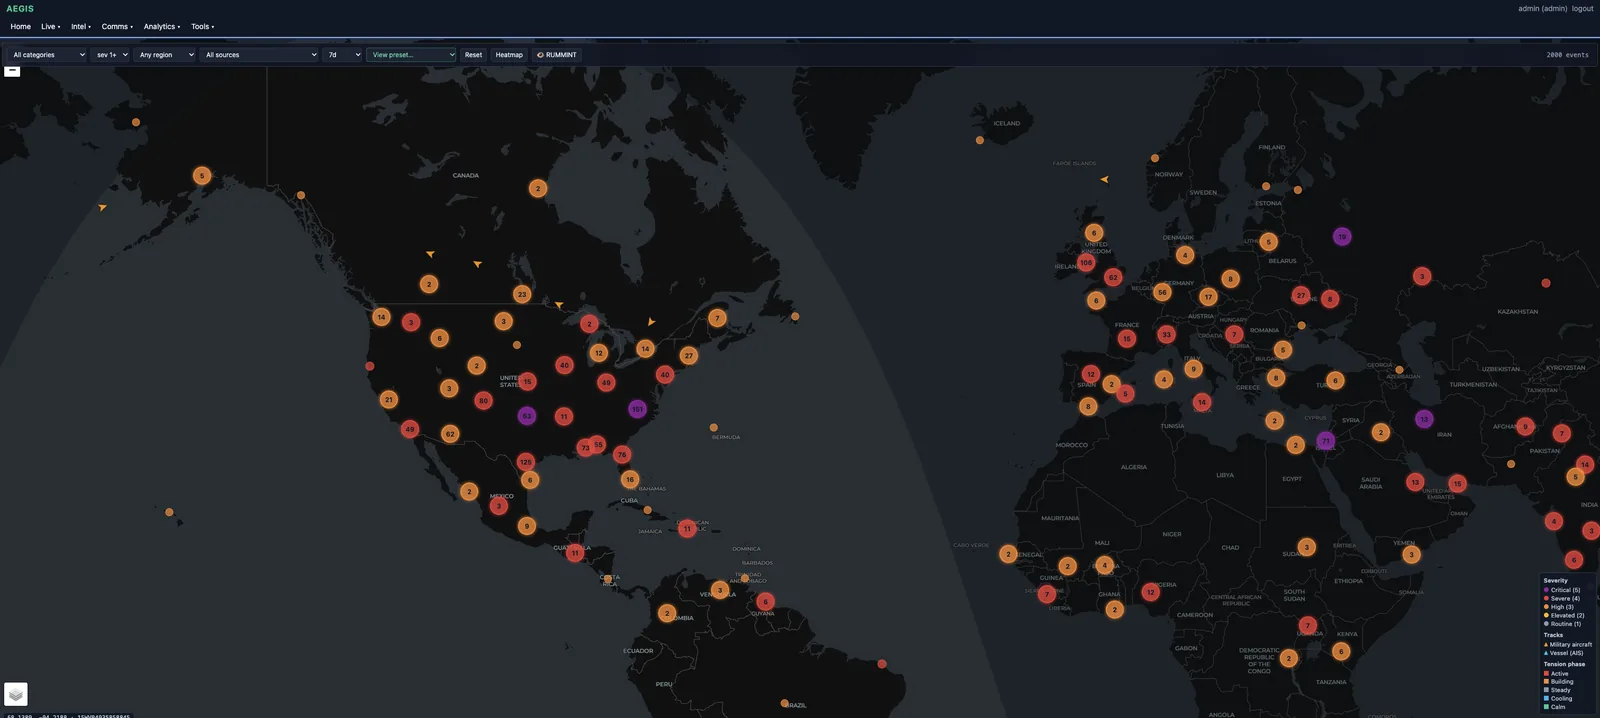
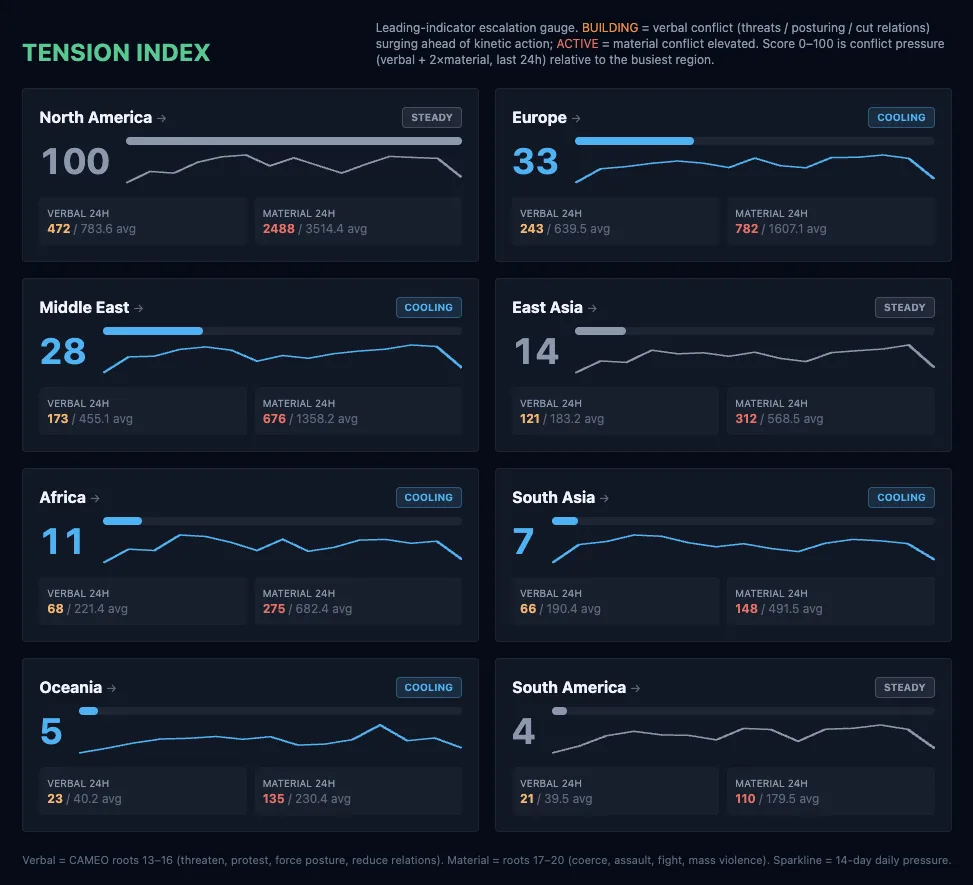
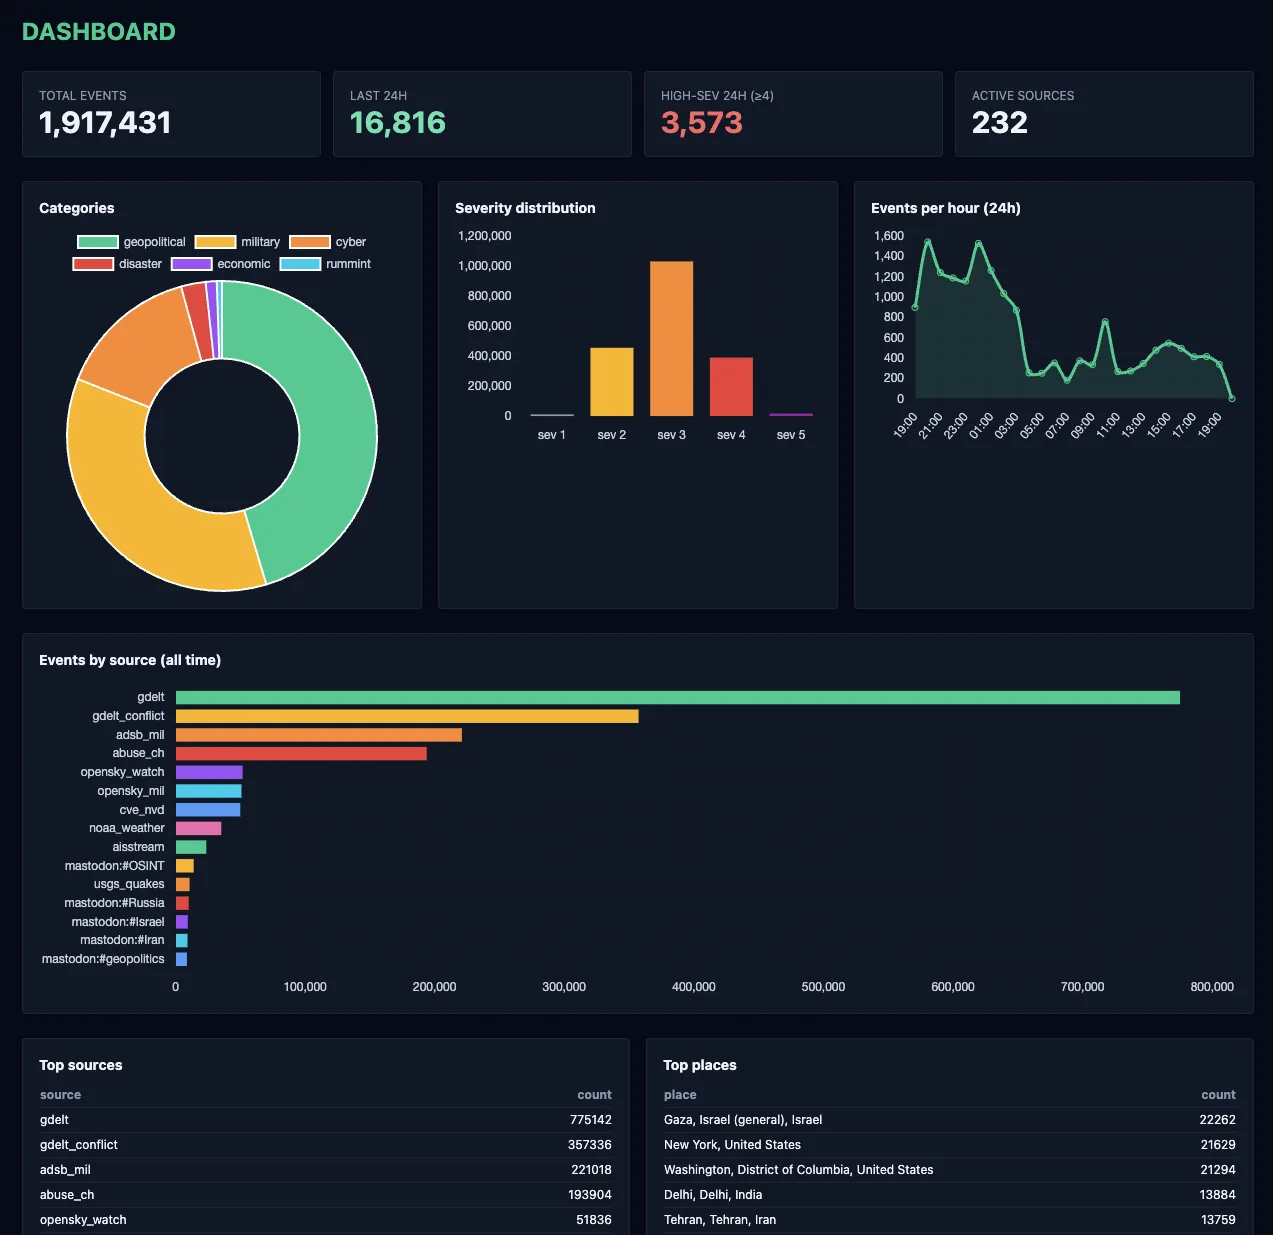
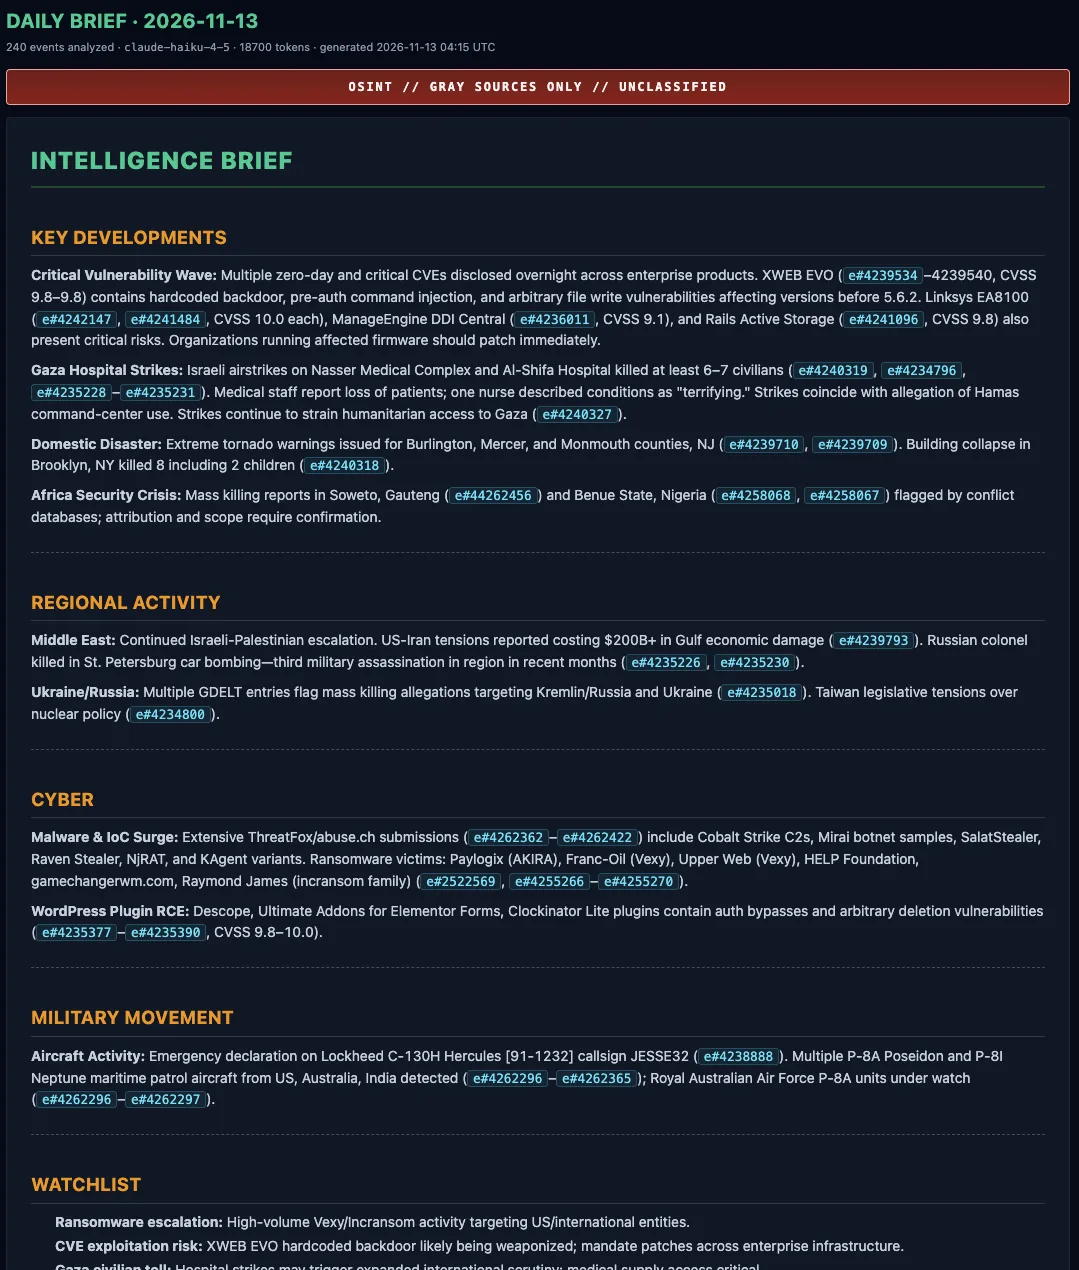
Aegis ingests the noisy outside world — global event data, military air and maritime tracking, CVE/KEV disclosure streams, ransomware victim feeds, dark-web channels, breach corpora — and turns it into something an operator can act on: ranked activity, cross-feed corroboration, a live severity-weighted map, and a regional tension index that separates verbal posturing from material conflict. Every morning it writes an intelligence brief in which every sentence cites its evidence, because intelligence without sourcing is just vibes.
The numbers
- 232 active sources, just under two million events and counting
- 670,000-indicator IOC corpus — domains, URLs, IPs, hashes, CVEs, emails
- Six live cyber feeds corroborated against each other, continuously
- A daily AI-written brief: hundreds of events analyzed, every claim pinned to its event ID
The arc
Aegis ran the path the Lab now runs on purpose: an idea argued into a thesis, a prototype ugly enough to be honest, an MVP that survived contact with real analysts, and a production system quietly deployed for several organizations since spring 2026. Privately hosted, deliberately boring to operate, built by people who carried pagers back when pagers were load-bearing. No booth, no magic quadrant, no growth team. It just runs.
Interested in a deployment? Write to the barn.